Scammers earned about $2 million in cash games using a virus
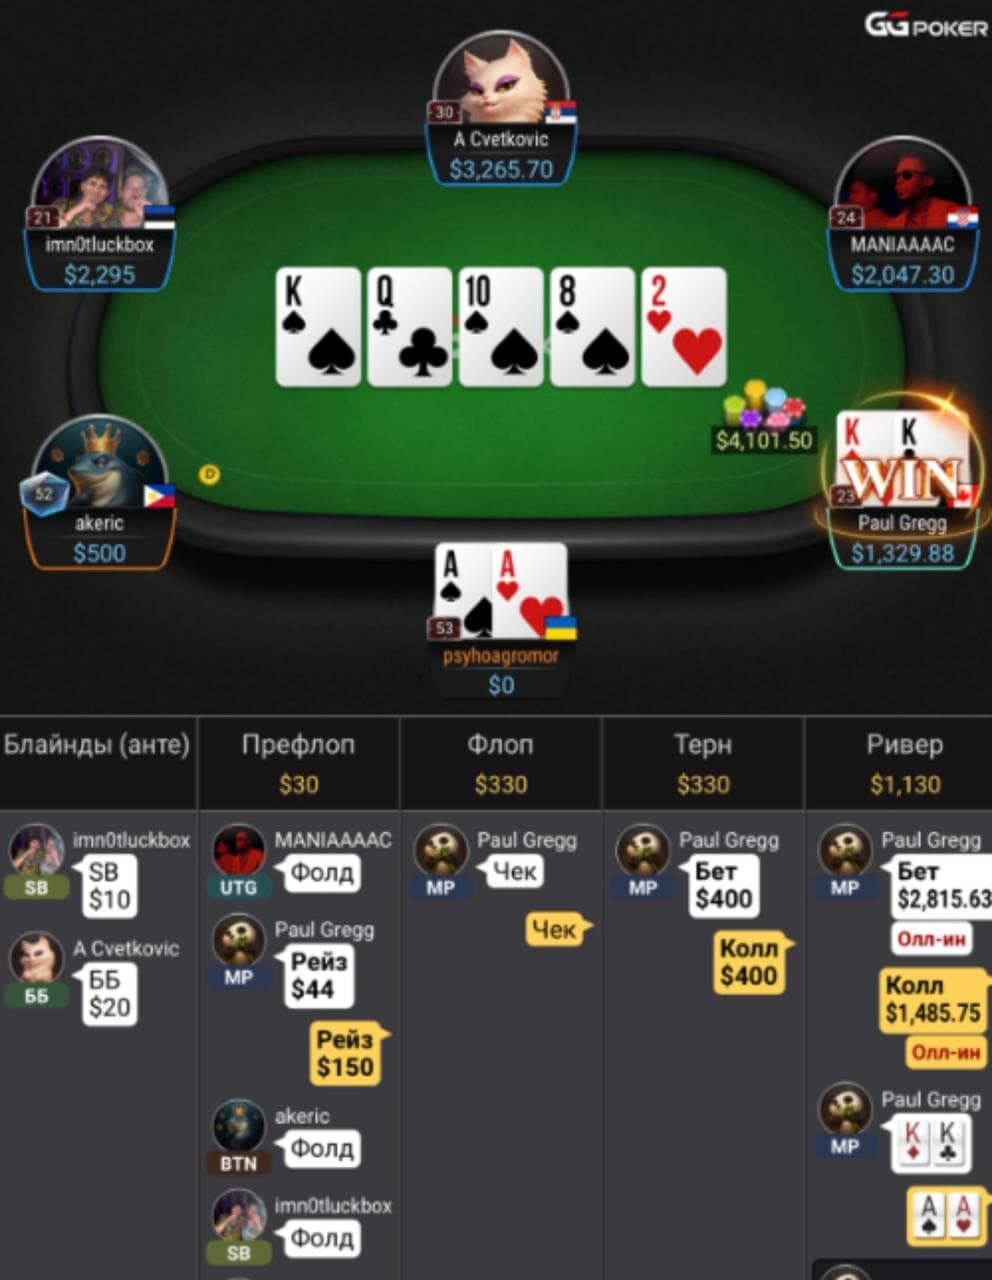
High-stakes cash game players have fallen victim to fraudsters. A scammer or group of criminals operated in major rooms, including GGPoker and ACR Poker, and thanks to a scheme involving a virus, managed to earn around $2 million over two years.
The fraudster turned out to be a player going by the nicknames Paul Gregg, Ez[Pz] and JackKlompus. The account OxOO is also linked to the scheme. This could be either another one of the scammer's nicknames or an accomplice. The fraudster turned the remote-access program MeshAgent into a trojan and somehow infected the computers of high-stakes cash game players with it.
The backdoor made it possible to see the victim's screen and hole cards in real time, and the trojan operated covertly, bypassing standard antivirus software.
Paul Gregg long tried not to draw attention to himself, but his winrate at stakes up to NL5000/NL10000 soared to anomalous levels. His play was marked by incredibly accurate calls and folds against opponents' bluffs.
One of the players discovered the trojan on his computer and found that it was transmitting data whenever Paul Gregg and OxOO were playing with him at the same table. During the investigation, evidence was gathered: MeshAgent logs, hand history and the timings of connections to the command servers. This data was passed on to the rooms, which permanently banned the fraudulent accounts and froze the funds in them to pay compensation to the victims.
The GTO or GTFO channel published a BAT file for finding traces of MeshAgent on your computer. If any are found, it is recommended to format the drive.
📰 Subscribe to Pokerflow